Trace each threat into its attack path, and enumerate the sources that detect it.
“The adversary suffers when they cannot hide, and every move is seen.”
Kestrel Orbital’s three departments share the Day-1 data model and a catalogue of four AN-THR threats. Today Dana Whitfield takes the lead for Satellite Design & Engineering: for every threat you enumerate its attack path as an AN-ATT element, then enumerate the sources needed to observe each step. The paths curate one normalized set of required data and signal sources and produce the attack-path elements and detection methods Executive Order 14144 requires for command and control.
DAY 3 START
Today you trace how an adversary would move through the telecommand path to realize each Day 2 threat, and name the data you would need to see each step. Yesterday Maya Reyes grounded the threats; today you work with Dana Whitfield, systems engineer in Satellite Design & Engineering. She wrote the update path an adversary would ride, and she has never had to describe it as an attacker would. Her build knowledge turns each threat into a walkable path, the department’s first full working day inside the shared model. The paths and the required sources they carry feed the detection methods Executive Order 14144 requires.
Set the context
Before you trace a single attack, fix what Day 2 handed you and today's job: the anchored threat set, and the task of showing how an adversary would actually move to realize each one.
MAP THE ATTACK PATHS
Six artifacts on the table. Satellite Design & Engineering owns the deepest knowledge of how the platform actually moves data and commands, and today the department lays that knowledge open: the six Kestrel Orbital artifacts below, brought to the table because two days of shared work earned the ask. You walk them together for every attack path you enumerate today; each tells you something different about where an attacker could enter, pivot, and what they would touch.
System block diagrams: what subsystem connects to what, over which bus, with which authentication boundary.
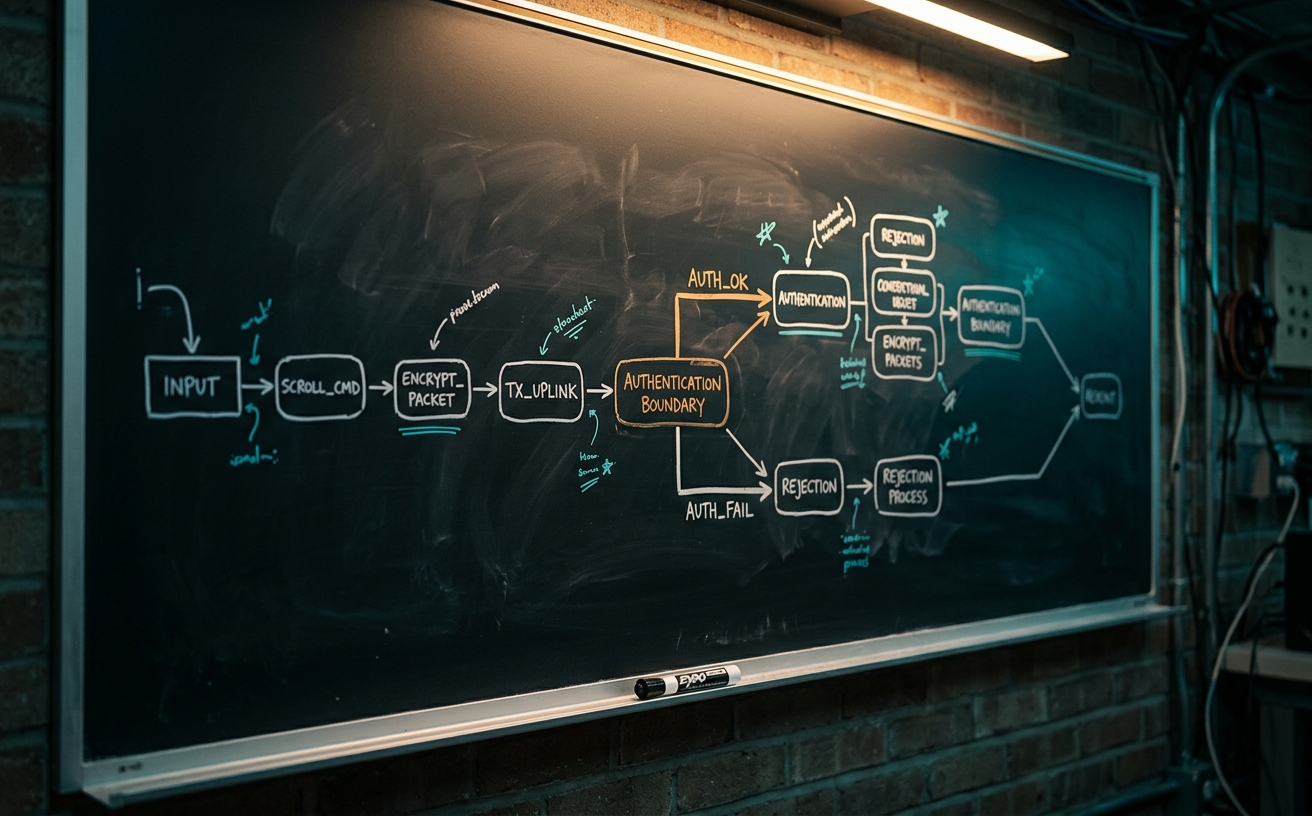
How a single telecommand actually moves from operator console through C&DH to the receiving subsystem.
How mission data moves on-board, where it’s buffered, where it’s signed, where it’s downlinked.
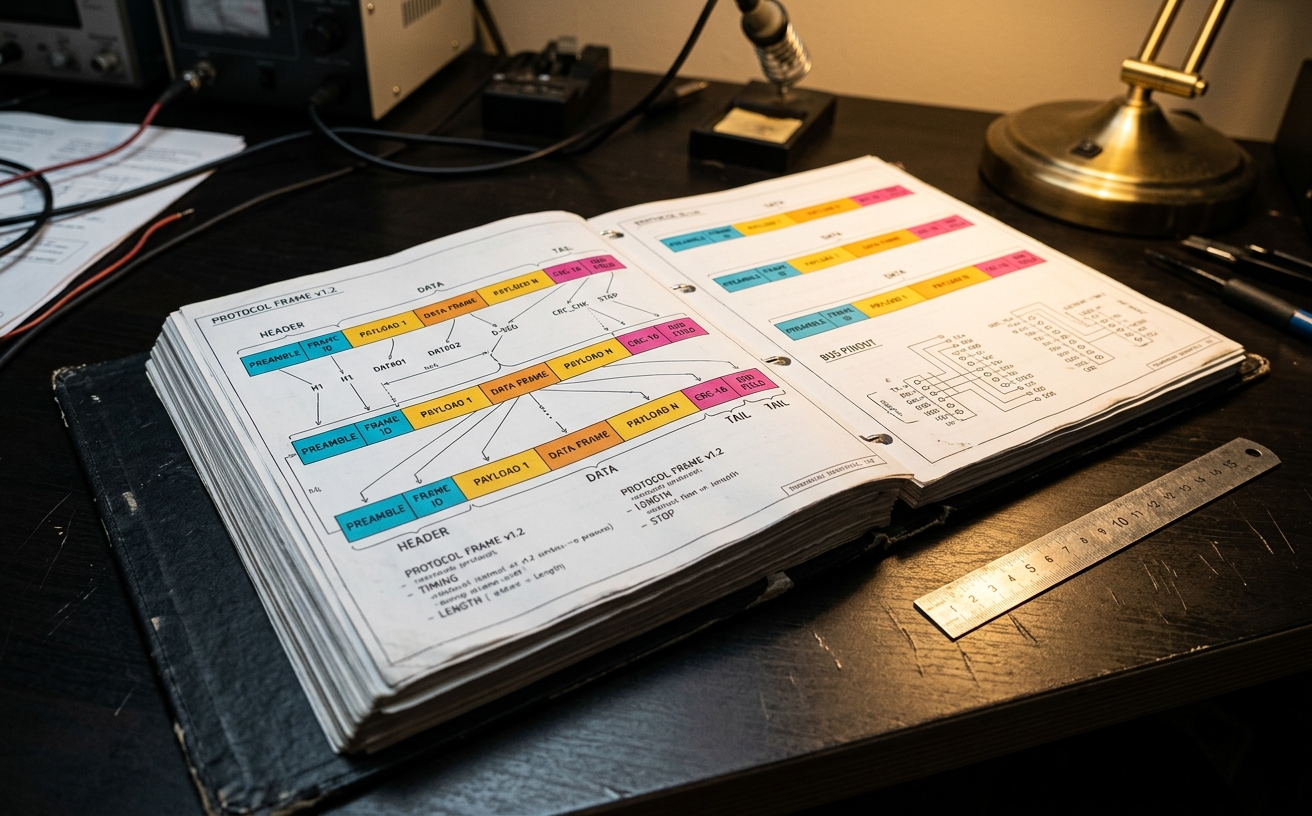
Wire-level protocol specs: CCSDS framing, MIL-STD-1553 bus traffic, SpaceWire, internal handshakes.
What runs on the OBC, how commands are parsed and dispatched, what behaviors are hard-coded vs reconfigurable.
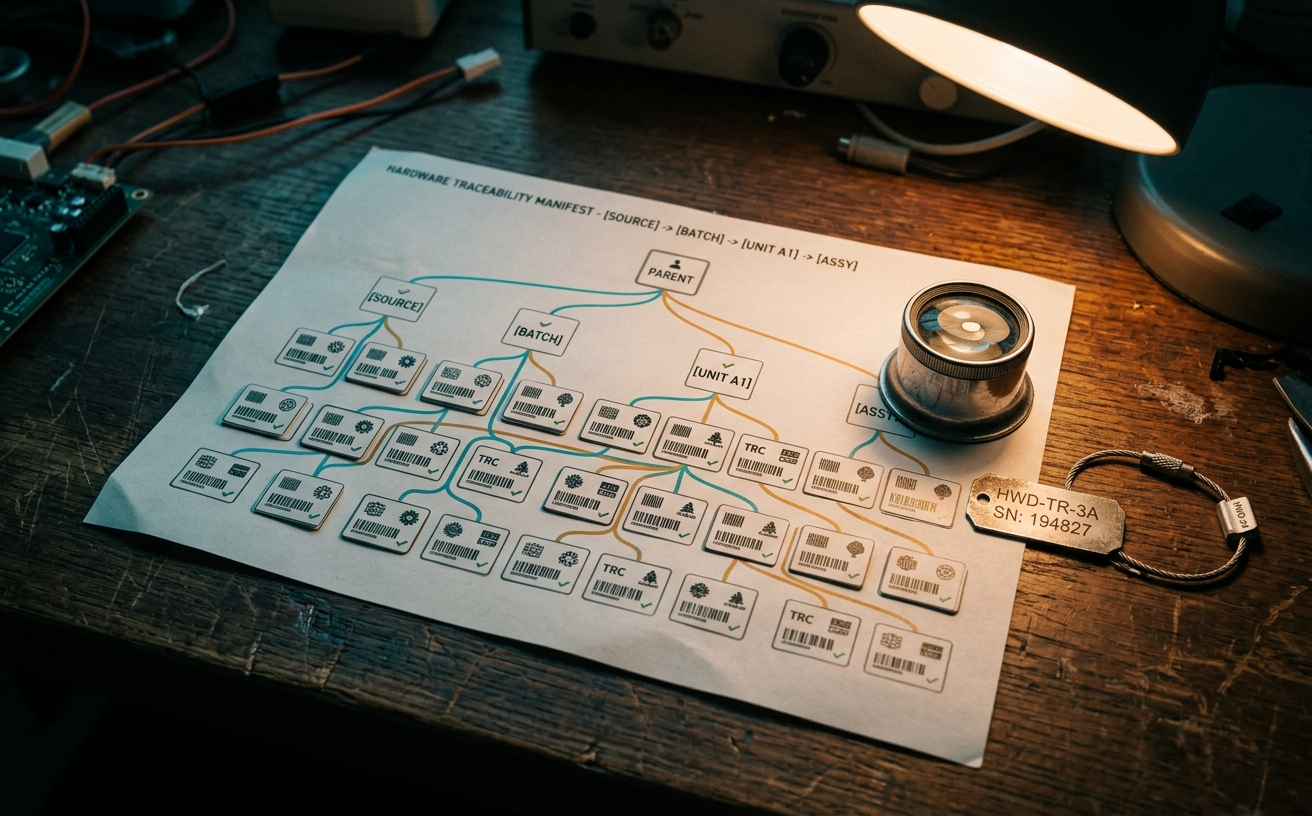
Vendor provenance for each firmware and hardware item: who built it, when, with which signing pipeline.
CHECKPOINT
Five questions on what Day 2 handed you and today’s job: the threat set you build on, the mandate the paths feed, and why Satellite Design & Engineering leads. Answer to confirm the context before you learn the method.
Learn the method
One repeatable way to turn a threat into a route: the AN-ATT enumeration, tracing the elements an adversary crosses from first access to objective, and naming the data that would reveal each step.
CONVERGED DETECTION ENGINEERING PROCESS
What you could not write on Monday: which elements sit between an adversary and the thing they want. You can now, because every one of them is named and parented. Eight steps, fixed order, one walk per path. A path inherits its threat’s TOE as its anchor, one element, so threat, path, signature and measure all name the same thing and one ordinal carries them. Where the route ends is the objective waypoint, and that may be a different element. Steps 07 and 08 are the ones teams drop: they turn “we should have logs” into named sources on named elements, each marked Available, Partial or Gap with an owner, so a missing source becomes a finding instead of a silence.
Fixed at AN. The layer settles one question before any other: is this part of the platform, or something you concluded about it? A path is a conclusion, so it never sits among the structural elements it crosses.
Day 1’s elements are the platform. A path is what the Security Operations Center and engineering concluded about moving through them, which is why it enters the analytic layer and never the decomposition.
CHECKPOINT
Five questions on converged detection engineering: what an AN-ATT path is, the one element it anchors to, the waypoints that describe the route, and the RDS and RSS required sources the element carries. Answer to confirm the method before you read the path set.
Enumerate the attack paths
Work segment by segment, Ground through Space. Each path anchors to the element its threat already names, traces the route an adversary would take to reach it as waypoints, then states on that same element the data and signal sources a defensive cyber operator must hold to see it.
ATTACK PATHS WALKED · 4 ELEMENTS
One attack path per Day-2 threat, walked with Satellite Design & Engineering. Every path names the entry, pivot, and objective the attacker would cross, anchors to its driving threat’s TOE wherever the route itself ends, and carries on that element the sources a defensive cyber operator must hold: RDS for what arrives as a record, RSS for what is measured in the physical layer.
 Ground
AN:ATT:Attack Path:00SVC:CP:Control Plane:08SVC:CP:Control Plane:09AST:SW:Software:03 Ground
AN:ATT:Attack Path:01AST:HW:Hardware:04AST:SW:Software:04SVC:CP:Control Plane:13 Link
AN:ATT:Attack Path:02SVC:HY:Hybrid:01SVC:HY:Hybrid:02AST:SI:Signal:00 Space
AN:ATT:Attack Path:03SVC:CP:Control Plane:04SVC:CP:Control Plane:02AST:FW:Firmware:01CHECKPOINT
Five questions on the set you built: the four paths, grounded versus hypothesis, coverage gaps, and what Day 4 does next. Answer to confirm the catalogue before you present it.
THE ATTACK-PATH CATALOGUE
THEORY TO TOOLING
What you built today does not stay in the classroom. The METEORSTORM vocabulary is a published taxonomy, and the moment the shift ends your work ships as machine tags the whole community can read.
TAG THE ATTACK PATHS
You can now show the route, not just the destination, and you can send it somewhere. METEORSTORM is what changed: each path names the elements an adversary crosses, in order, in a published vocabulary, so Kestrel’s MISP instance and any threat intel platform that imports the taxonomy already read it, out to the Space ISAC exchange. One path carries four things. Click through them, then follow the strip below to see where the record goes.
Every path names one element it is about, and it is the element its threat already named. That is what keeps the week joined up: yesterday’s threat, today’s path, tomorrow’s signature and Friday’s measure all point at the same service.
Target and objective are not the same thing. The target says what the path is about; the objective says where the route ends. Here they are different elements, and that is normal. A path that can name no element at all is excluded on the record, with the reason.
SVC:CP:Control Plane:09, ground command acceptance, the service that decides who may commandAN:THR:Threat:00, Day 2’s threat, which named that same elementAST:SW:Software:03, the patch deployment pipelinemeteorstorm vocabulary you just tagged it with.SVC-CP onto their own control-plane services, and what they send back is routed to whoever owns the element it names.DAY 3 COMPLETE
You mapped 4 attack paths with Dana Whitfield and Satellite Design & Engineering, each traced through the CONOPS with the detection sources needed to see it. Dana knows where the sources are thin. Tomorrow you take the paths back to Maya Reyes, and Day 4 writes the detection signatures and response playbooks that fire on them.
DAY 3 COMPLETE
What you built today. Four AN-ATT elements enumerated with Dana Whitfield and Satellite Design & Engineering. 2 GROUND, 1 LINK, 1 SPACE. Every element walks an end-to-end attacker traversal through real services and assets on the platform, anchored to public reporting or framework reference. No hypothetical paths; every element is grounded. Satellite Design & Engineering spent the day writing in the language it helped build, and the other two departments can read every path without a briefing. The paths and the RDS and RSS required sources they carry feed the detection methods Executive Order 14144 requires on the command path.
INCIDENT RESPONSE
PREPARATION.
Day 3 is complete: four attack paths enumerated against the command path and the data each would expose, with Satellite Design & Engineering walking every chain beside you. Tomorrow, Incident Response Preparation: you turn today’s paths into the signatures that fire so IR knows which playbook to run.
Defense became a route the team can watch. Each path names the parts an attacker crosses, so they know exactly where to place detection.